Ready for NIS2, without a consultant
Normatik prepares every NIS2 measure for you: policies, risks and a step-by-step plan in plain language. Fill it in yourself, or we’ll do it with you.
Prefer to call? +31 88 42 42 042

NIS2 affects more organisations than you think
The Dutch implementation of NIS2 (Cyberbeveiligingswet) applies to medium-sized and large organisations in 18 sectors. Smaller organisations are often affected by it through their customers, who are also required to evaluate their suppliers.
Which 18 sectors?
Annex 1 — Essential sectors
Annex 2 — Important sectors
Not sure? Let us find out.
NIS2 check
Your organisation probably falls under NIS2 itself
Then the ten cybersecurity risk-management measures and an incident reporting obligation apply, and the board is ultimately responsible. In 20 minutes we show you how to handle this with Normatik.
Book a 20-minute call → Explore the 10 measures firstWe are happy to work out with you whether your sector is covered
The sector classification is not always obvious. In a short call we look at your activities and tell you honestly whether the law applies to you.
Let us find out → View the 18 sectorsYour customers will set requirements for you
Organisations covered by the law must assess their suppliers. They want to see that you have mapped your risks, that you assess your own suppliers and that you can demonstrate which measures you have taken. With Normatik Starter (€149/month) you record all of that in one place and show it as soon as someone asks.
Discuss what you need → Compare the plansYou are probably not covered yourself, but check your customers
If your customers are covered, they may ask for proof that you work securely. We are happy to think it through with you.
Ask your question → Read about supply chain securityYou probably aren't subject to the law
Information security is still a good idea, and customers and insurers are increasingly addressing these issues. Normatik makes it very easy to get started.
Compare the plans → Still have a question? Get in touchIndicative, not legal advice. Some organisations fall under the law regardless of their size.
We manage the Dutch National Register of Deceased Persons, so we don’t entrust our information security to just anyone. With 42 and Normatik, we know it’s in good hands.


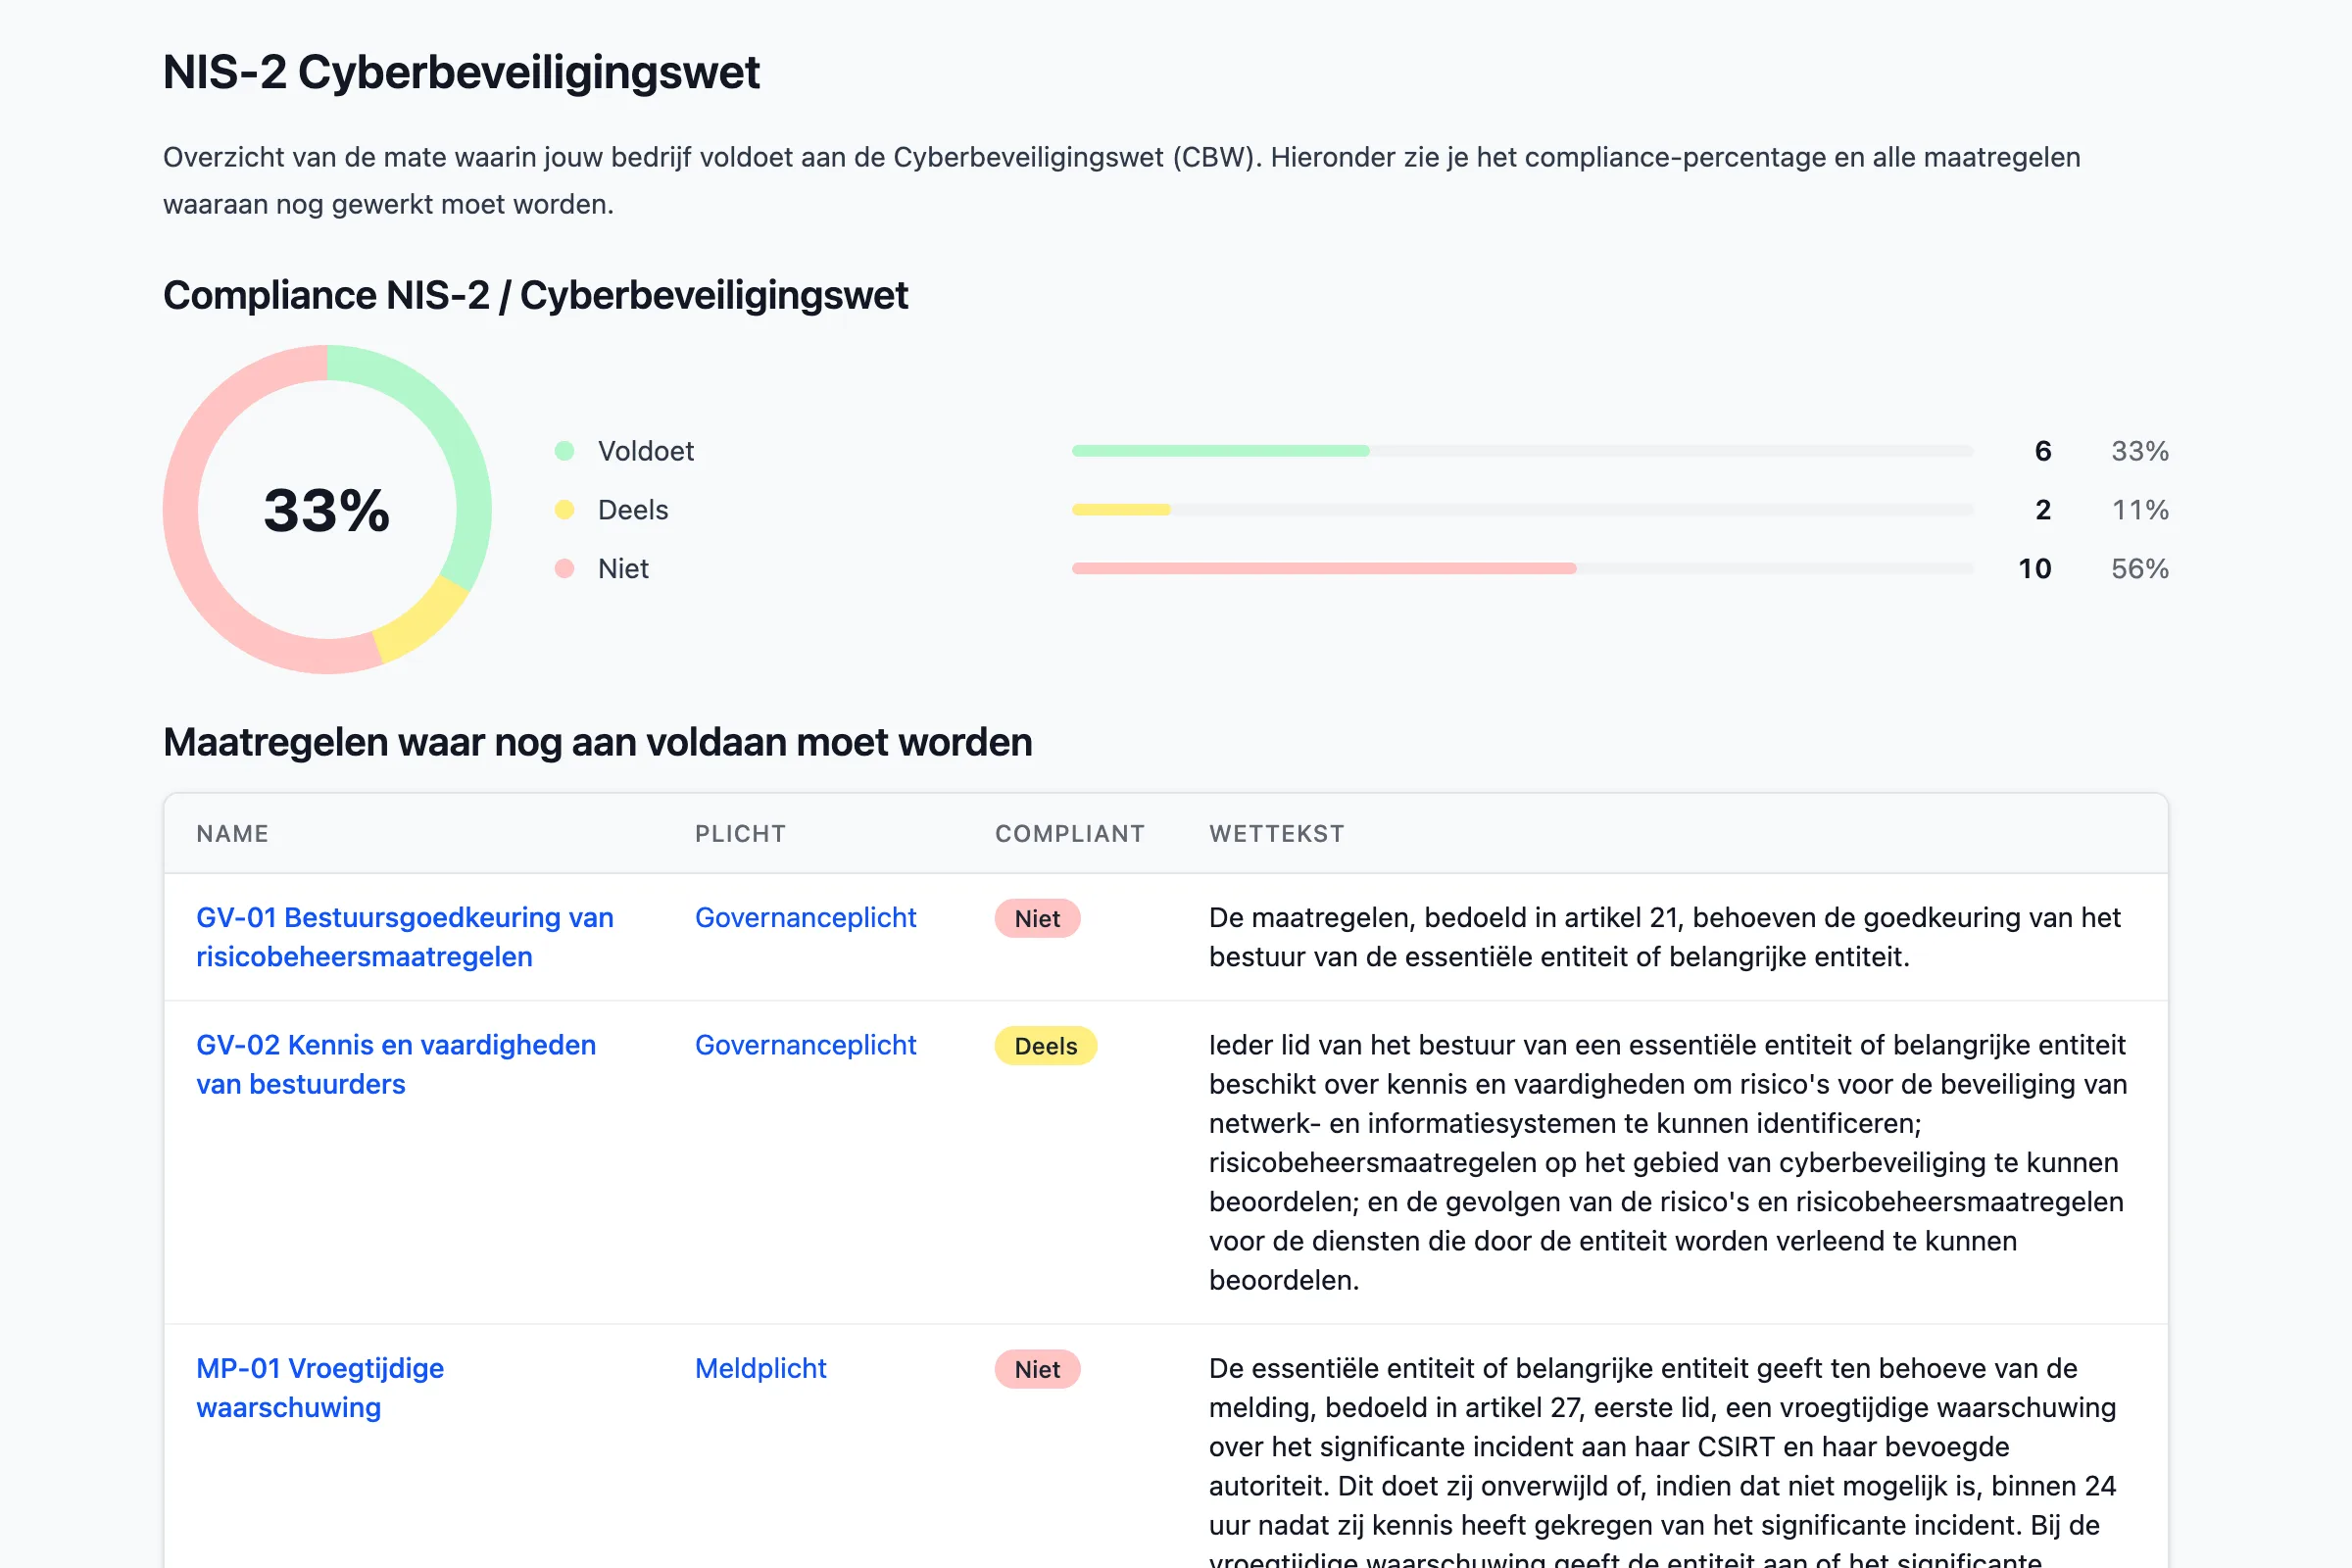
Where other tools give you a blank canvas, Normatik comes filled with everything you need. All you have to do is review it and adapt it to your situation.

Policies are ready to use
All required policy documents are drafted and pre-filled. From risk policies to cryptography policies — you only need to review and publish them.

Risks have already been identified
The most common risks for SMEs are already in the system, including threats and control measures. Adjust them where needed.

In plain language
No security jargon or technical terminology. Normatik explains everything in plain language so that everyone can work with it.

Step-by-step guidance
Normatik tells you exactly what to do and when. Follow the path, tick off each step and build your ISMS — without outside help.

A fraction of the cost
While a consultant costs €10,000 or more, Normatik starts at €149/month. Everything the consultant would deliver is already in the platform.

Always know where you stand
Your dashboard shows your progress and remaining tasks in real time. Face your next audit with confidence.
Whether you are a small supplier or a large MSP — Normatik grows with you. No hidden costs or surprises.
Starter
For SME suppliers that need a compliance application to meet supply chain requirements.
- ✓ Access to the full application
- ✓ Basic policy templates
- ✓ A dashboard showing your progress
- ✓ You complete everything yourself
- ✓ Need help? Purchase support at a fixed hourly rate
Professional
We take care of everything. All you need to become compliant — set up and guided by us.
- ✓ Everything in Starter
- ✓ Extended templates
- ✓ Asset module
- ✓ Setup support (fixed hours)
- ✓ Introductory NIS2 training for management
- ✓ Content review
Enterprise
For larger organisations that want to manage other certifications, such as ISO 27001 or DORA, alongside NIS2.
- ✓ Everything in Professional
- ✓ Complete setup support
- ✓ Multiple standards (ISO / DORA / NEN / BIO)
- ✓ API access for integrations
Normatik guides you through the ten cybersecurity risk-management measures of Article 21 — from risk analysis to incident handling. Templates, checklists and explanations are ready for every measure.
Explore all 10 measures →Normatik gives you real digital independence. Data is stored within Europe, without dependence on American tech giants or other external parties.
Maximum control
Your data always remains yours. No hidden data transfers or unwanted third-party access.
Better compliance
Fully aligned with European privacy legislation. No concerns about data transfers outside the EU.
Always an alternative
Our solution is built so that every component has alternatives — you stay in control, now and in the future.
Hosted in the Netherlands
All your data is stored in Dutch data centres that run on reused energy. Waste heat is used to heat buildings — no new data centres or carbon credits, but real impact.
GDPR compliant
Maximum compliance with European privacy legislation. Your data never leaves the European Union.
No vendor lock-in
Alternatives exist for every component. You are never dependent on a single supplier or technology.
The latest on NIS2 & security


You do not have to figure it out alone. Book a free 20-minute introductory call and discover how Normatik has already done the hard work for you. No obligations or commitments.
Book a 20-minute call →